Penetration Testing
AI agents continuously find and investigate vulnerabilities. Experienced human testers confirm what’s exploitable and uncover the risks automation alone misses.
Book a demo

Trusted by Customers
Know what an attacker could actually do
Scanners tell you what might be wrong. A penetration test shows what can be exploited, how far an attacker could get, and what to fix first.

Find real, exploitable risk
Our testers prove which vulnerabilities can be exploited in your environment, so your team stops chasing false positives.

Meet audit and customer requirements
FedRAMP and CMMC Level 3 require penetration testing, SOC 2 and ISO 27001 auditors expect it, and enterprise security reviews almost always ask for a recent report.

Stay secure between annual tests
AI agents keep testing as your applications and infrastructure change, instead of leaving you exposed for the eleven months between point-in-time tests.
Continuous agentic testing
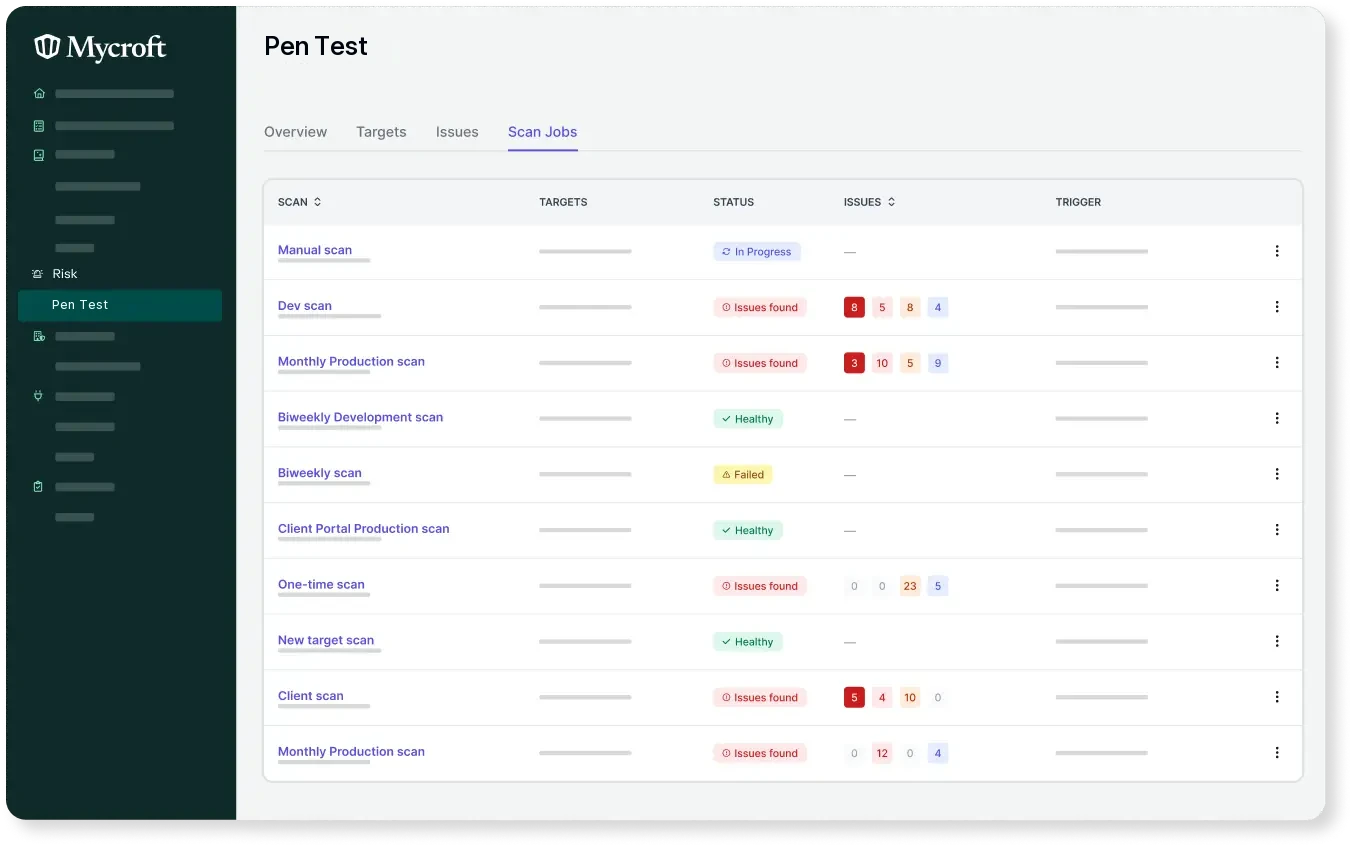
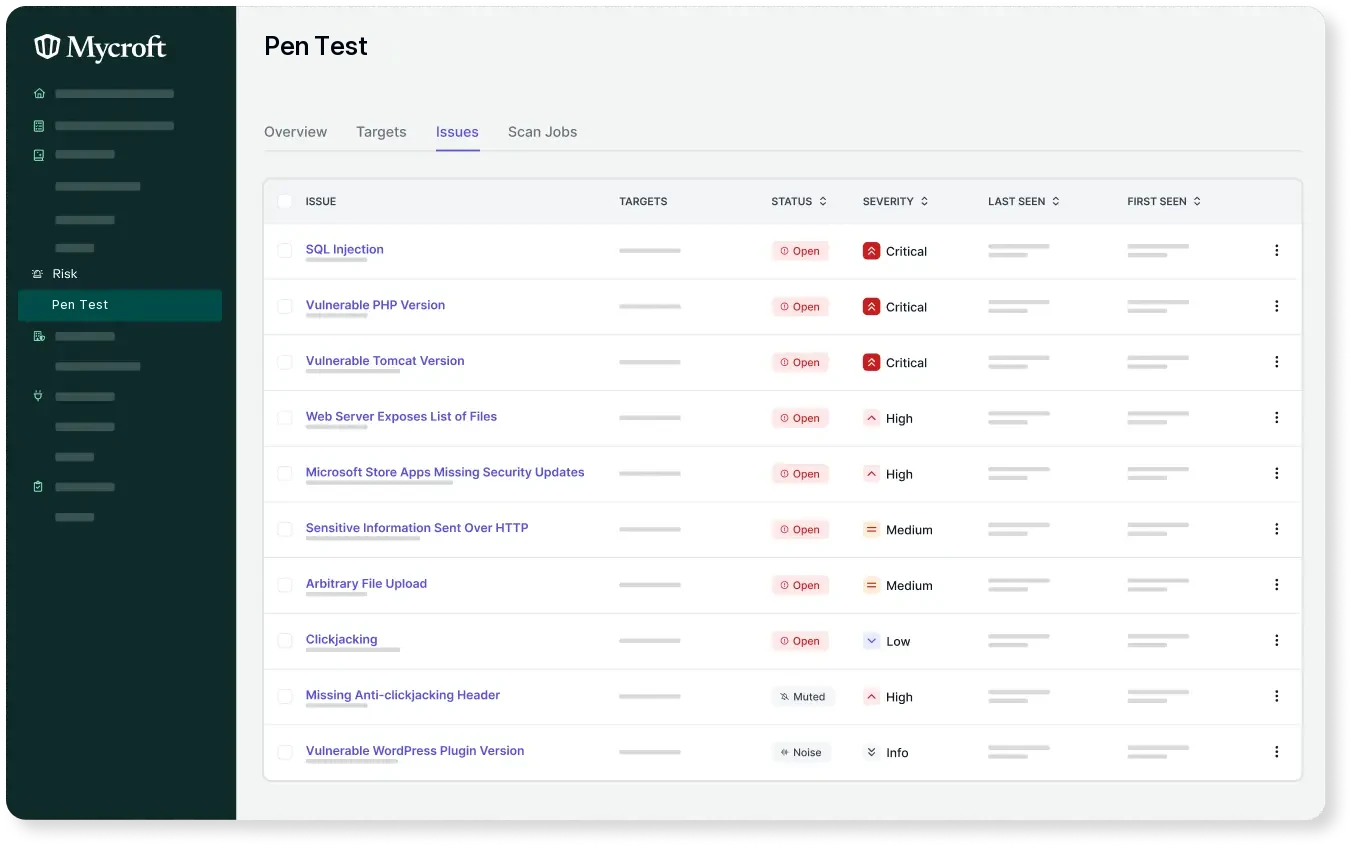
Mycroft’s AI agents continuously probe your applications, APIs, and cloud infrastructure, then investigate each potential vulnerability to see whether it can be exploited and chained with others.
Human-validated findings
Experienced penetration testers review what the agents find, confirm real-world exploitability, and test the areas automation struggles with, such as business logic flaws and authorization bypasses.
Prioritized remediation
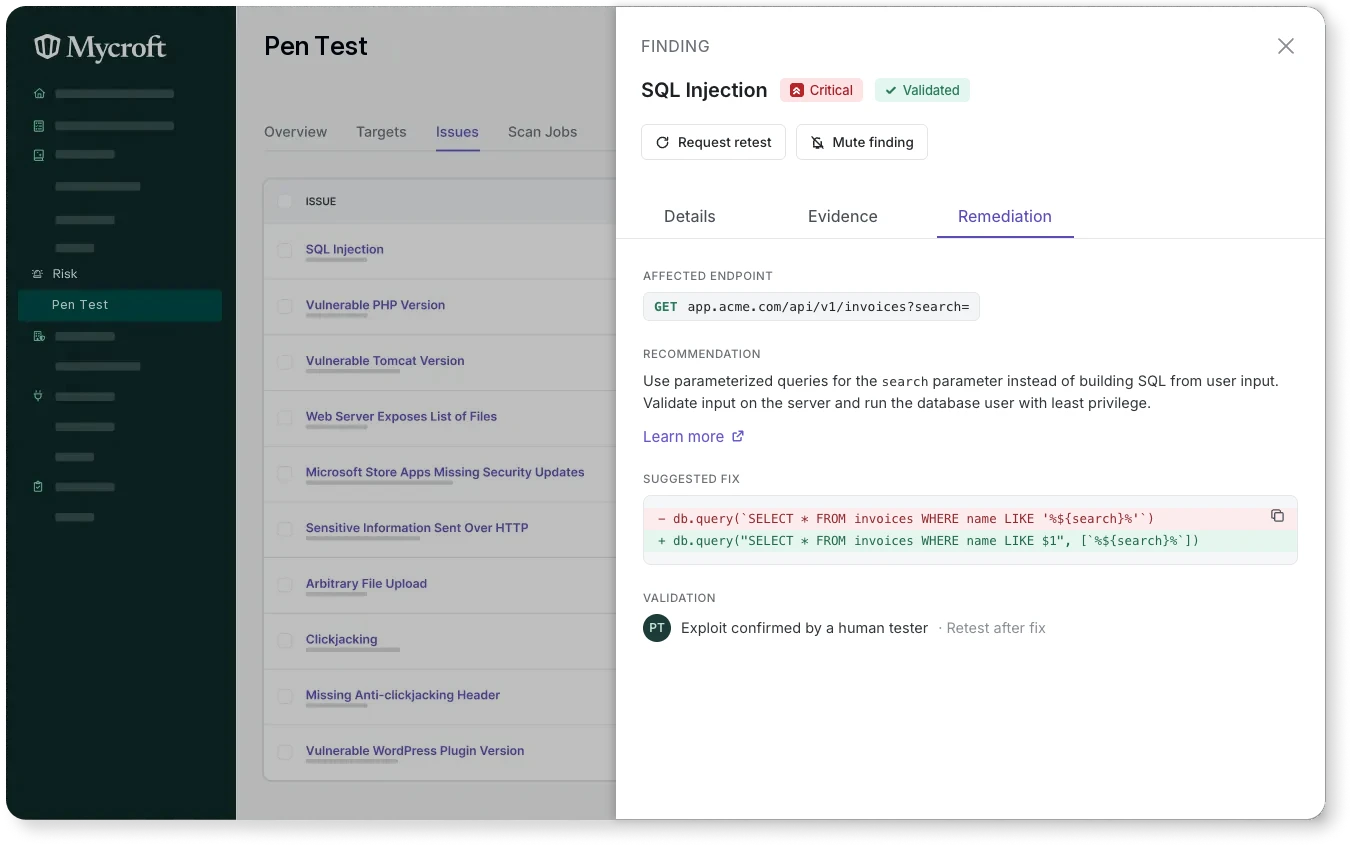
Every confirmed finding comes with its severity, evidence of the exploit, and clear guidance on how to fix it, so your team knows exactly where to start.
Platform features
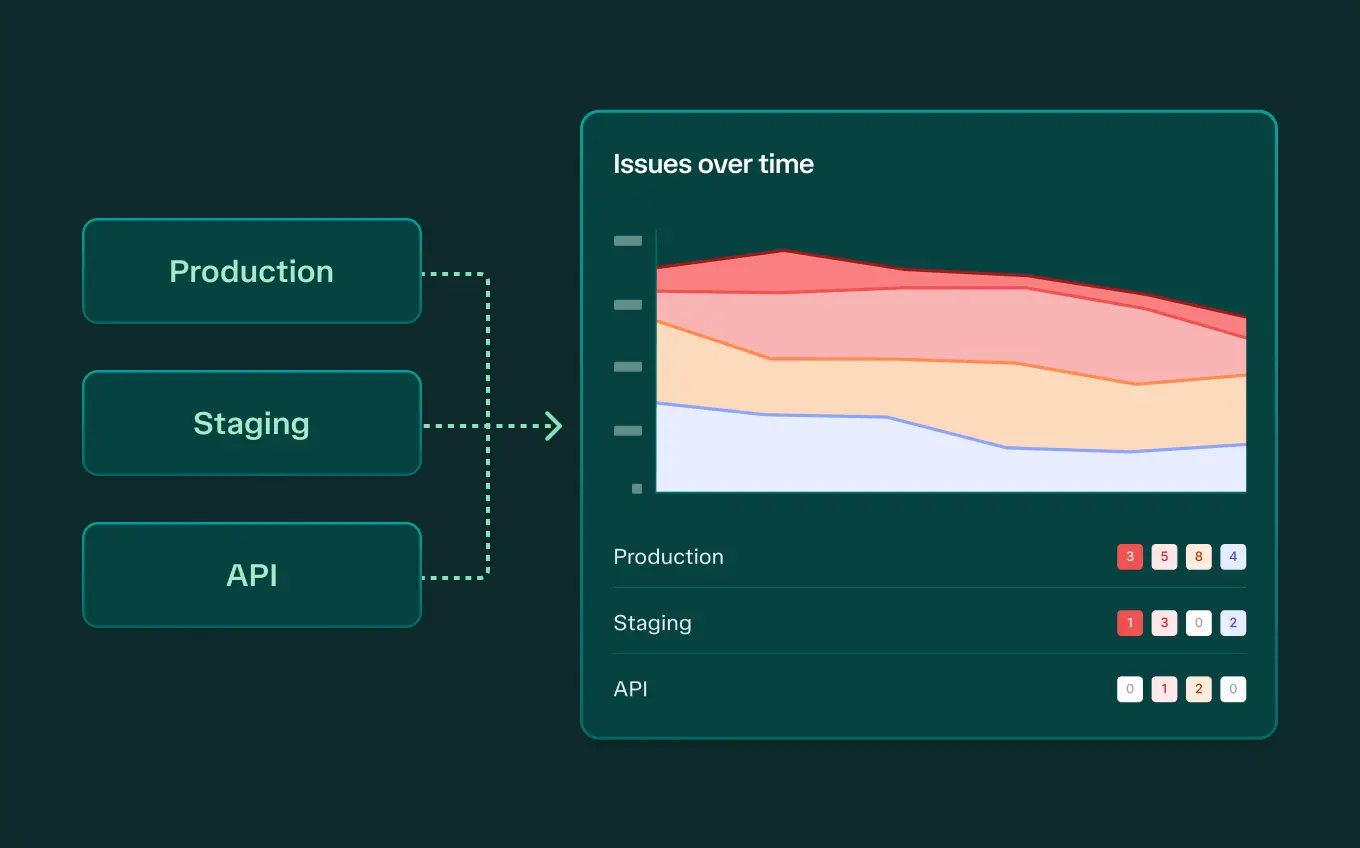
Testing across your whole attack surface
From the web app your customers log in to, to the cloud it runs on, to the devices you ship.
Web applications and APIs
Authentication, access control, injection, and business logic testing for your web apps and APIs.
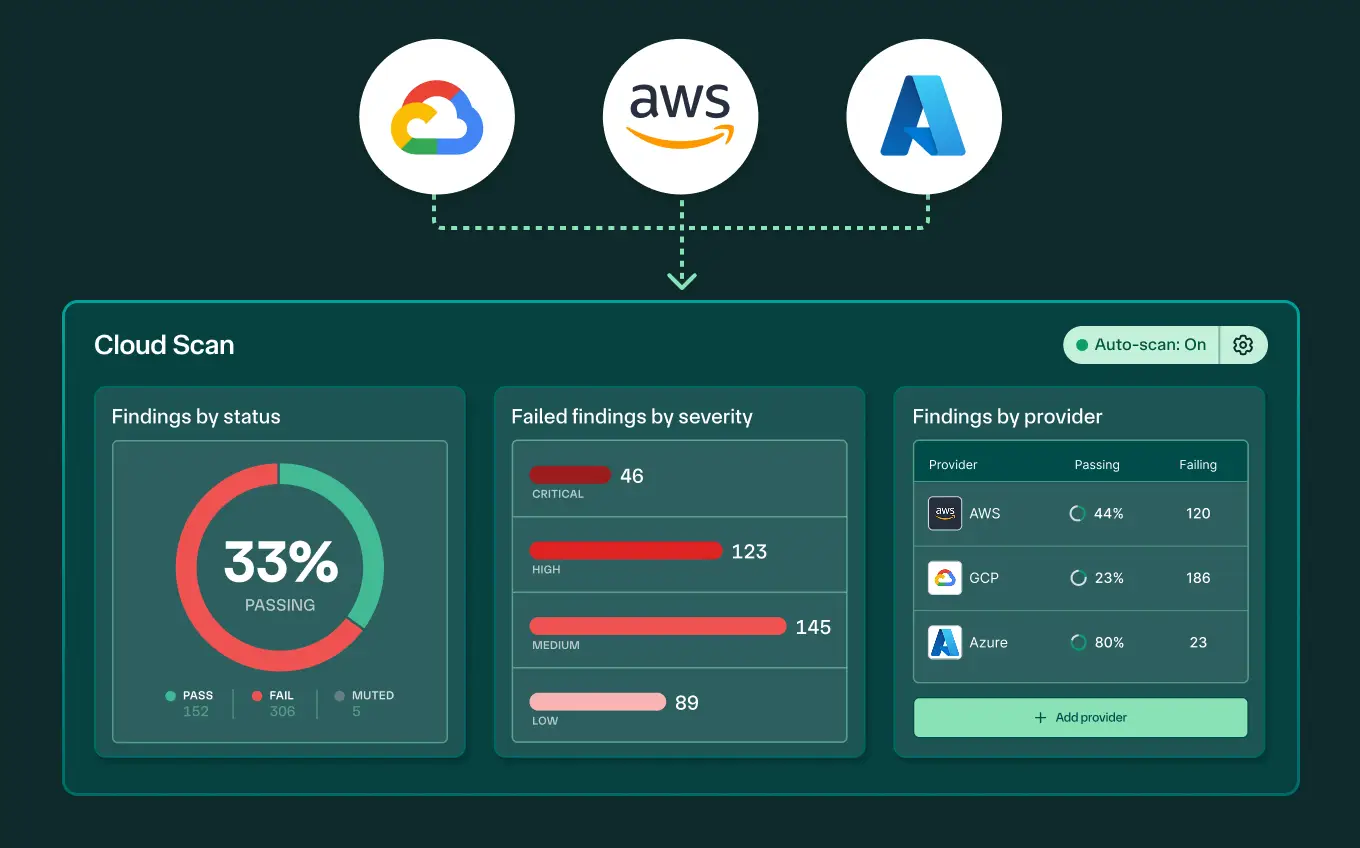
Cloud infrastructure
Misconfigurations, exposed services, and privilege escalation paths across your cloud environment.
Hardware and embedded devices
Firmware, interfaces, and communications testing for the hardware and embedded devices you build.
Book a demo

Client Testimonial
“
Thank you! Your pentest report was critical.”
Elliot Dohm
Co-Founder & CTO of Page
Read the latest insights from our experts
Stay secure with expert, data-driven resources to strengthen your security knowledge and ensure compliance confidence.


Frequently asked questions
What’s the difference between a vulnerability scan and a penetration test?
How do AI agents and human testers work together?
Which compliance frameworks require a penetration test?
What do you test?
How often should we run a penetration test?
We turn the compliance nightmare into a dream
Book a demo